Enterprise governance by design.
Deliver secure, maintainable applications with role-based permissions, identity integration, governed workflows, and auditability — built in, not bolted on.
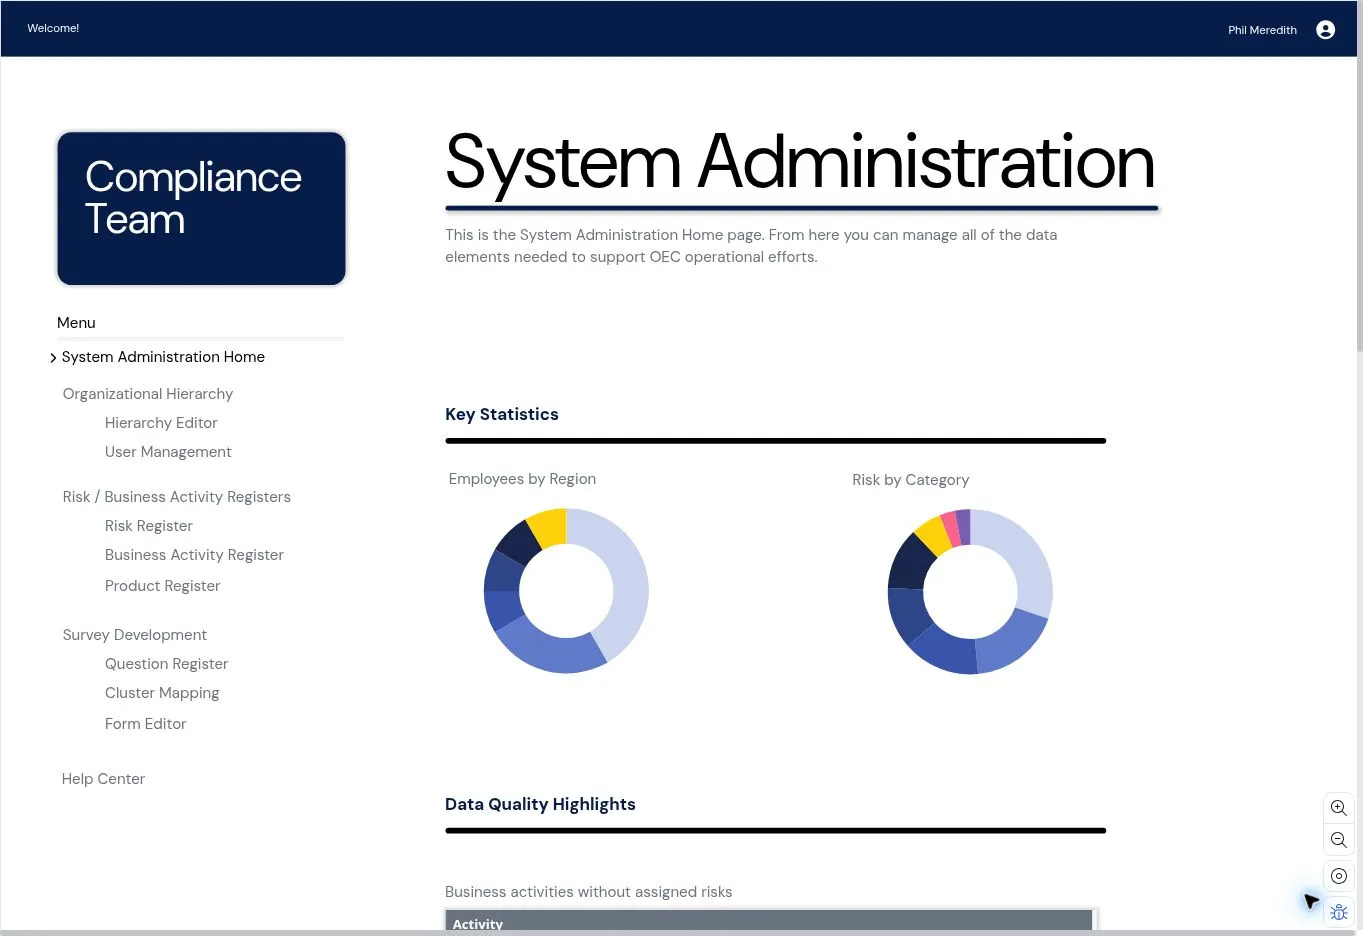
Deliver secure, maintainable applications with role-based permissions, identity integration, governed workflows, and auditability — built in, not bolted on.
What’s built in
Control who can see, decide, and act at every step of an application or workflow.
Work with your existing identity provider so access follows your enterprise policies.
Approval and process rules are enforced in the workflow itself, not left to manual handoffs.
Keep a clear record of decisions, approvals, and actions for accountability and review.
Apply the same governance model across every application you build.
Shared components and central control make applications easier to support.
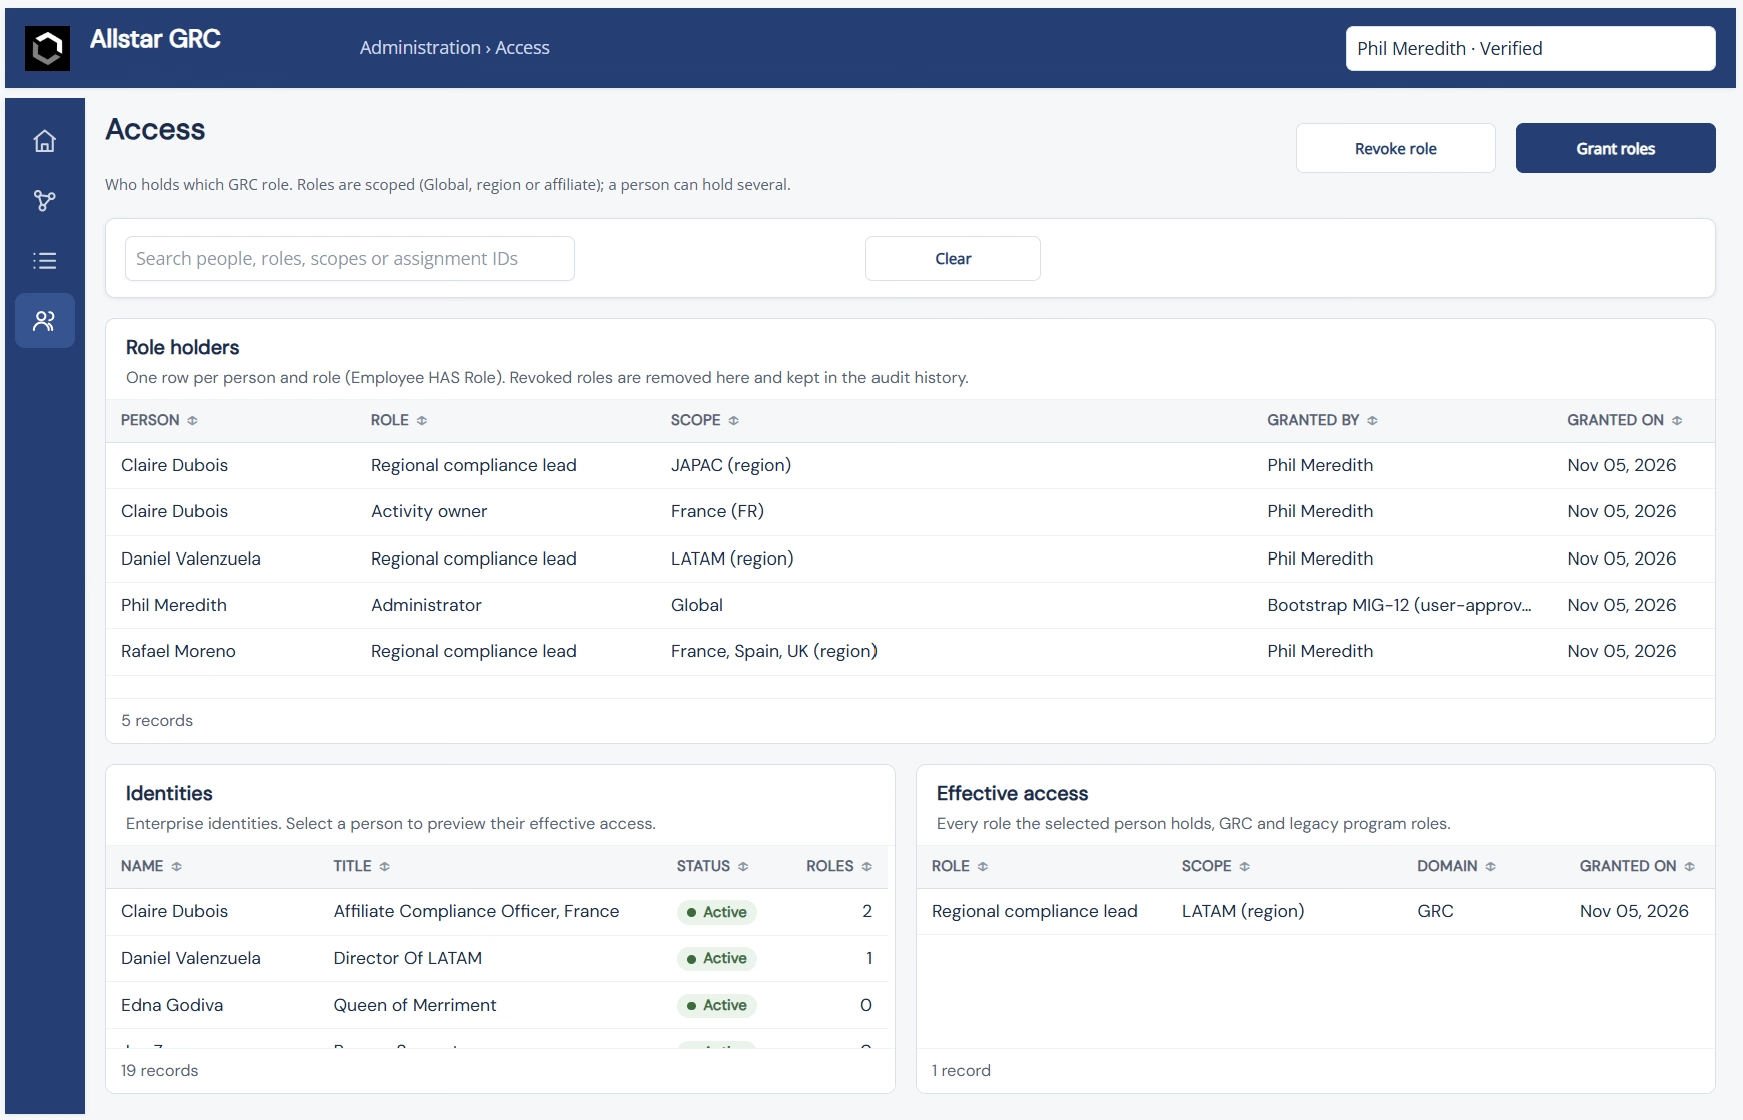
Access
Permissions follow people and roles across applications, data, and workflow steps.
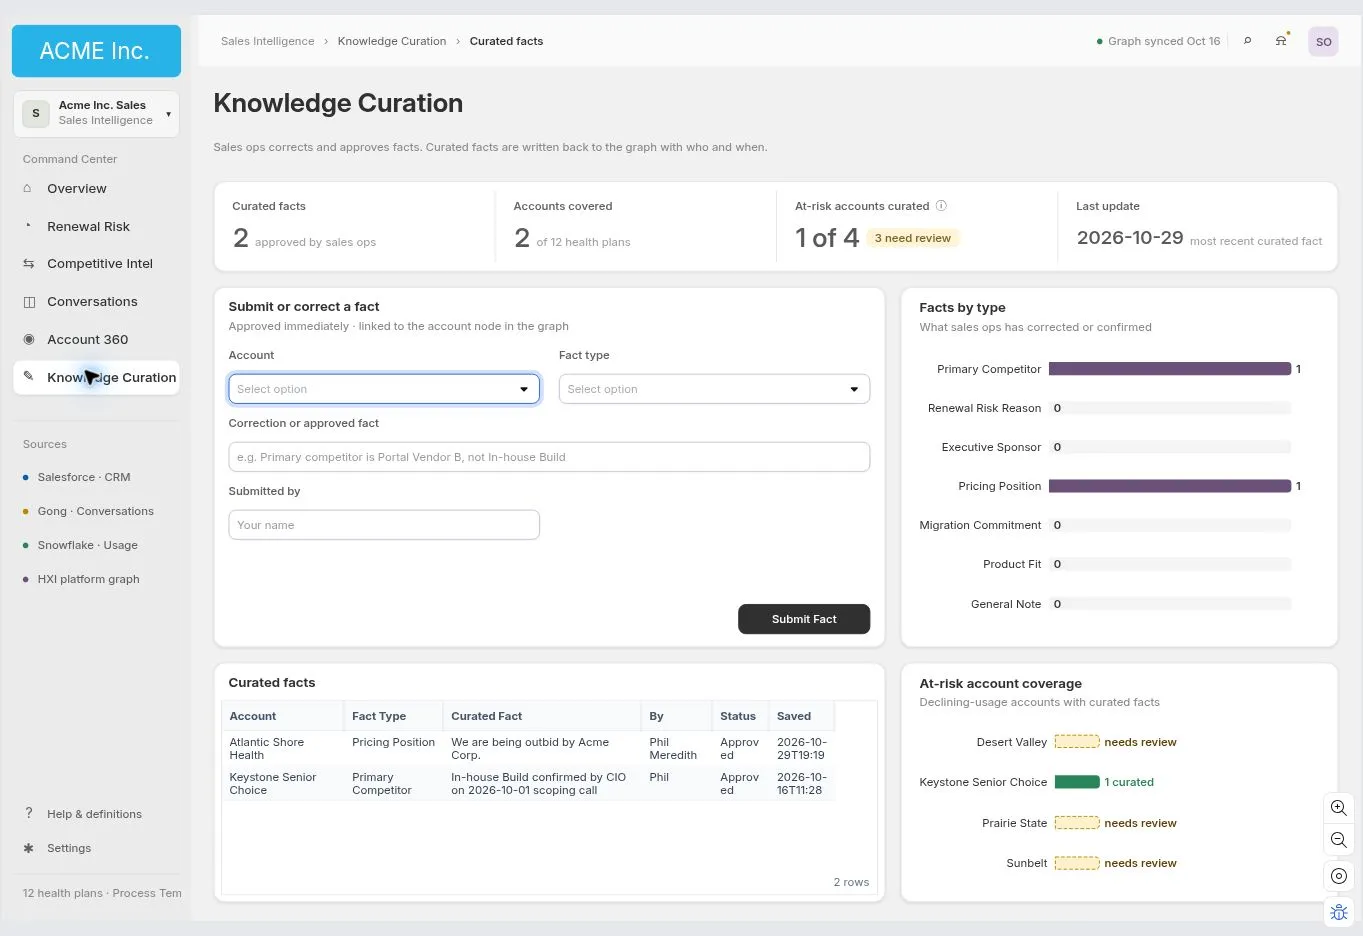
Accountability
Know who approved what, when, and what happened as a result.
Model governed processes with approvals, assignments, and exception handling.
Learn moreBuild operational applications with low-code/no-code tools and reusable components.
Learn moreWe’ll walk your architecture and security teams through how Jupiter fits your controls.