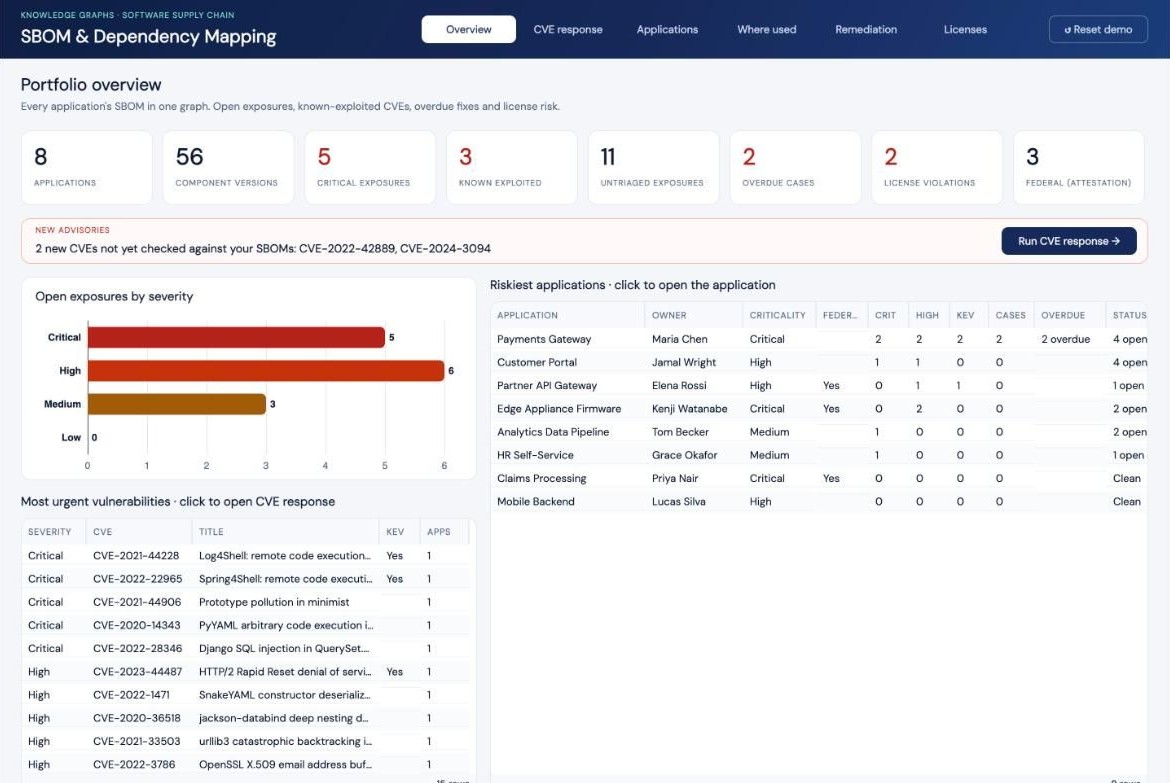
Overview
Ingest SBOMs in CycloneDX and SPDX formats into a knowledge graph of applications, components, versions, licenses and vulnerabilities. When a new CVE is published, security teams find every affected application and owner in seconds, track remediation, and answer SBOM and secure-software attestation requests from U.S. federal customers.
Key capabilities
- Graph exploration
- Remediation workflow
- SBOM ingestion
- Vulnerability matching
- License compliance